

Background
CVE-2025–0133 is a reflected cross-site scripting (XSS) vulnerability affecting Palo Alto Networks’ PAN-OS software, specifically within the GlobalProtect gateway and portal features. This flaw poses a risk to organisations using GlobalProtect for remote access, particularly those with Clientless VPN enabled.
The vulnerability was discovered externally and publicly disclosed in May 2025. While its severity is rated as low or medium, the potential for phishing and credential theft makes it a concern for any organisation relying on GlobalProtect for secure remote connectivity.
Risk
This vulnerability allows attackers to execute malicious JavaScript in the browser of an authenticated user who clicks on a specially crafted link. The script runs in the context of the GlobalProtect Captive Portal, making the attack appear legitimate and increasing the likelihood of success.
The primary risk lies in phishing attacks. An attacker could craft a link that appears to originate from the organisation’s GlobalProtect portal, tricking users into entering credentials or other sensitive information.
Check if You’re Affected
You can test if your system is affected by modifying the following proof of concept example URL before accessing it via a web browser:
https://<Palo Alto GlobalProtect URL>/ssl-vpn/getconfig.esp?client-type=1&protocol-version=p1&app-version=3.0.1-10&clientos=Linux&os-version=linux-64&hmac-algo=sha1%2Cmd5&enc-algo=aes-128-cbc%2Caes-256-cbc&authcookie=12cea70227d3aafbf25082fac1b6f51d&portal=us-vpn-gw-N&user=%3Csvg%20xmlns%3D%22http%3A%2F%2Fwww.w3.org%2F2000%2Fsvg%22%3E%3Cscript%3Eprompt(%22XSS%22)%3C%2Fscript%3E%3C%2Fsvg%3E&domain=(empty_domain)&computer=computer
If your system is susceptible, you’ll receive a prompt with “XSS” in the heading when the page loads.

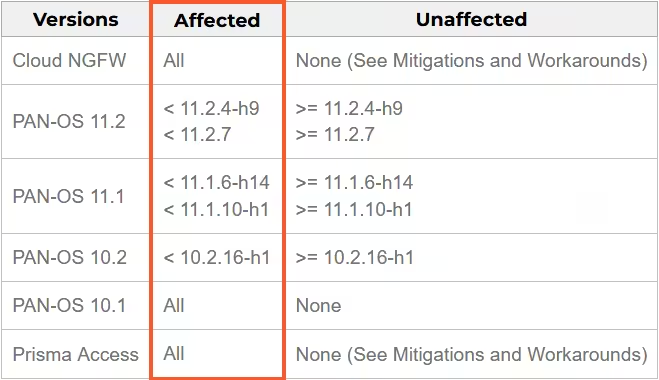
The Palo Alto Networks Security Advisory for CVE-2025-0133 also provides the following table listing affected product versions:
Solution
Palo Alto Networks has released updates to address CVE-2025–0133. Organisations should upgrade to the following PAN-OS versions or later:
- PAN-OS 11.2: Upgrade to 11.2.4-h9 or 11.2.7
- PAN-OS 11.1: Upgrade to 11.1.6-h14 or 11.1.10-h1
- PAN-OS 10.2: Upgrade to 10.2.16-h1
If you are using GlobalProtect with Clientless VPN enabled, consider disabling it if not strictly necessary. This reduces the risk of credential theft associated with this vulnerability.
For full details and guidance, refer to the Palo Alto Networks Security Advisory for CVE-2025-0133.
Conclusion
While CVE-2025–0133 may not be critical in terms of system integrity or availability, it highlights the importance of regular vulnerability assessments and proactive patching. Attackers often exploit low-severity issues to gain initial access or harvest credentials for further attacks.
At Evolve North, we offer comprehensive CREST accredited penetration testing and vulnerability scanning services tailored to your organisation’s needs. Our testers simulate real-world attack scenarios to uncover weaknesses before attackers do. Whether you’re looking to assess your remote access infrastructure, web applications, or internal network, we provide clear, actionable insights to help you strengthen your cyber security posture.
If you’re unsure about any of these instructions, please contact us on 01748 905 002 or email info@evolvenorth.com, we’re happy to help.